Cybersecurity for modern digital products requires constant oversight: even after successful testing, new releases and code changes can introduce new vulnerabilities.
That’s why businesses are increasingly supplementing traditional security checks with the bug bounty model — a program in which a company gives independent ethical hackers access to search for vulnerabilities in its systems and pays a reward for confirmed findings.
Staying ahead of such threats is exactly what HackenProof — a cybersecurity and bug bounty platform — does. According to the company, the combined asset value and market capitalization of the products whose security HackenProof helps ensure exceeds $95 billion.
15 Vulnerabilities per 1,000 Lines of Code: Why Business Needs Continuous Oversight
On average, during active development of a complex product, 15 to 30 vulnerabilities emerge per 1,000 lines of code, and at least 1–2 of them are critical, according to HackenProof.
The rise of AI agents has made these risks more tangible. In 2025, Anthropic, the American AI company, recorded what it assessed as the first AI-orchestrated cyberattack, in which an autonomous agent independently carried out an estimated 80–90% of the work: scanning systems, exploiting vulnerabilities, and stealing credentials. At the same time, a Thales report showed that AI-driven bot attacks increased 12.5 times over the previous year in 2025.
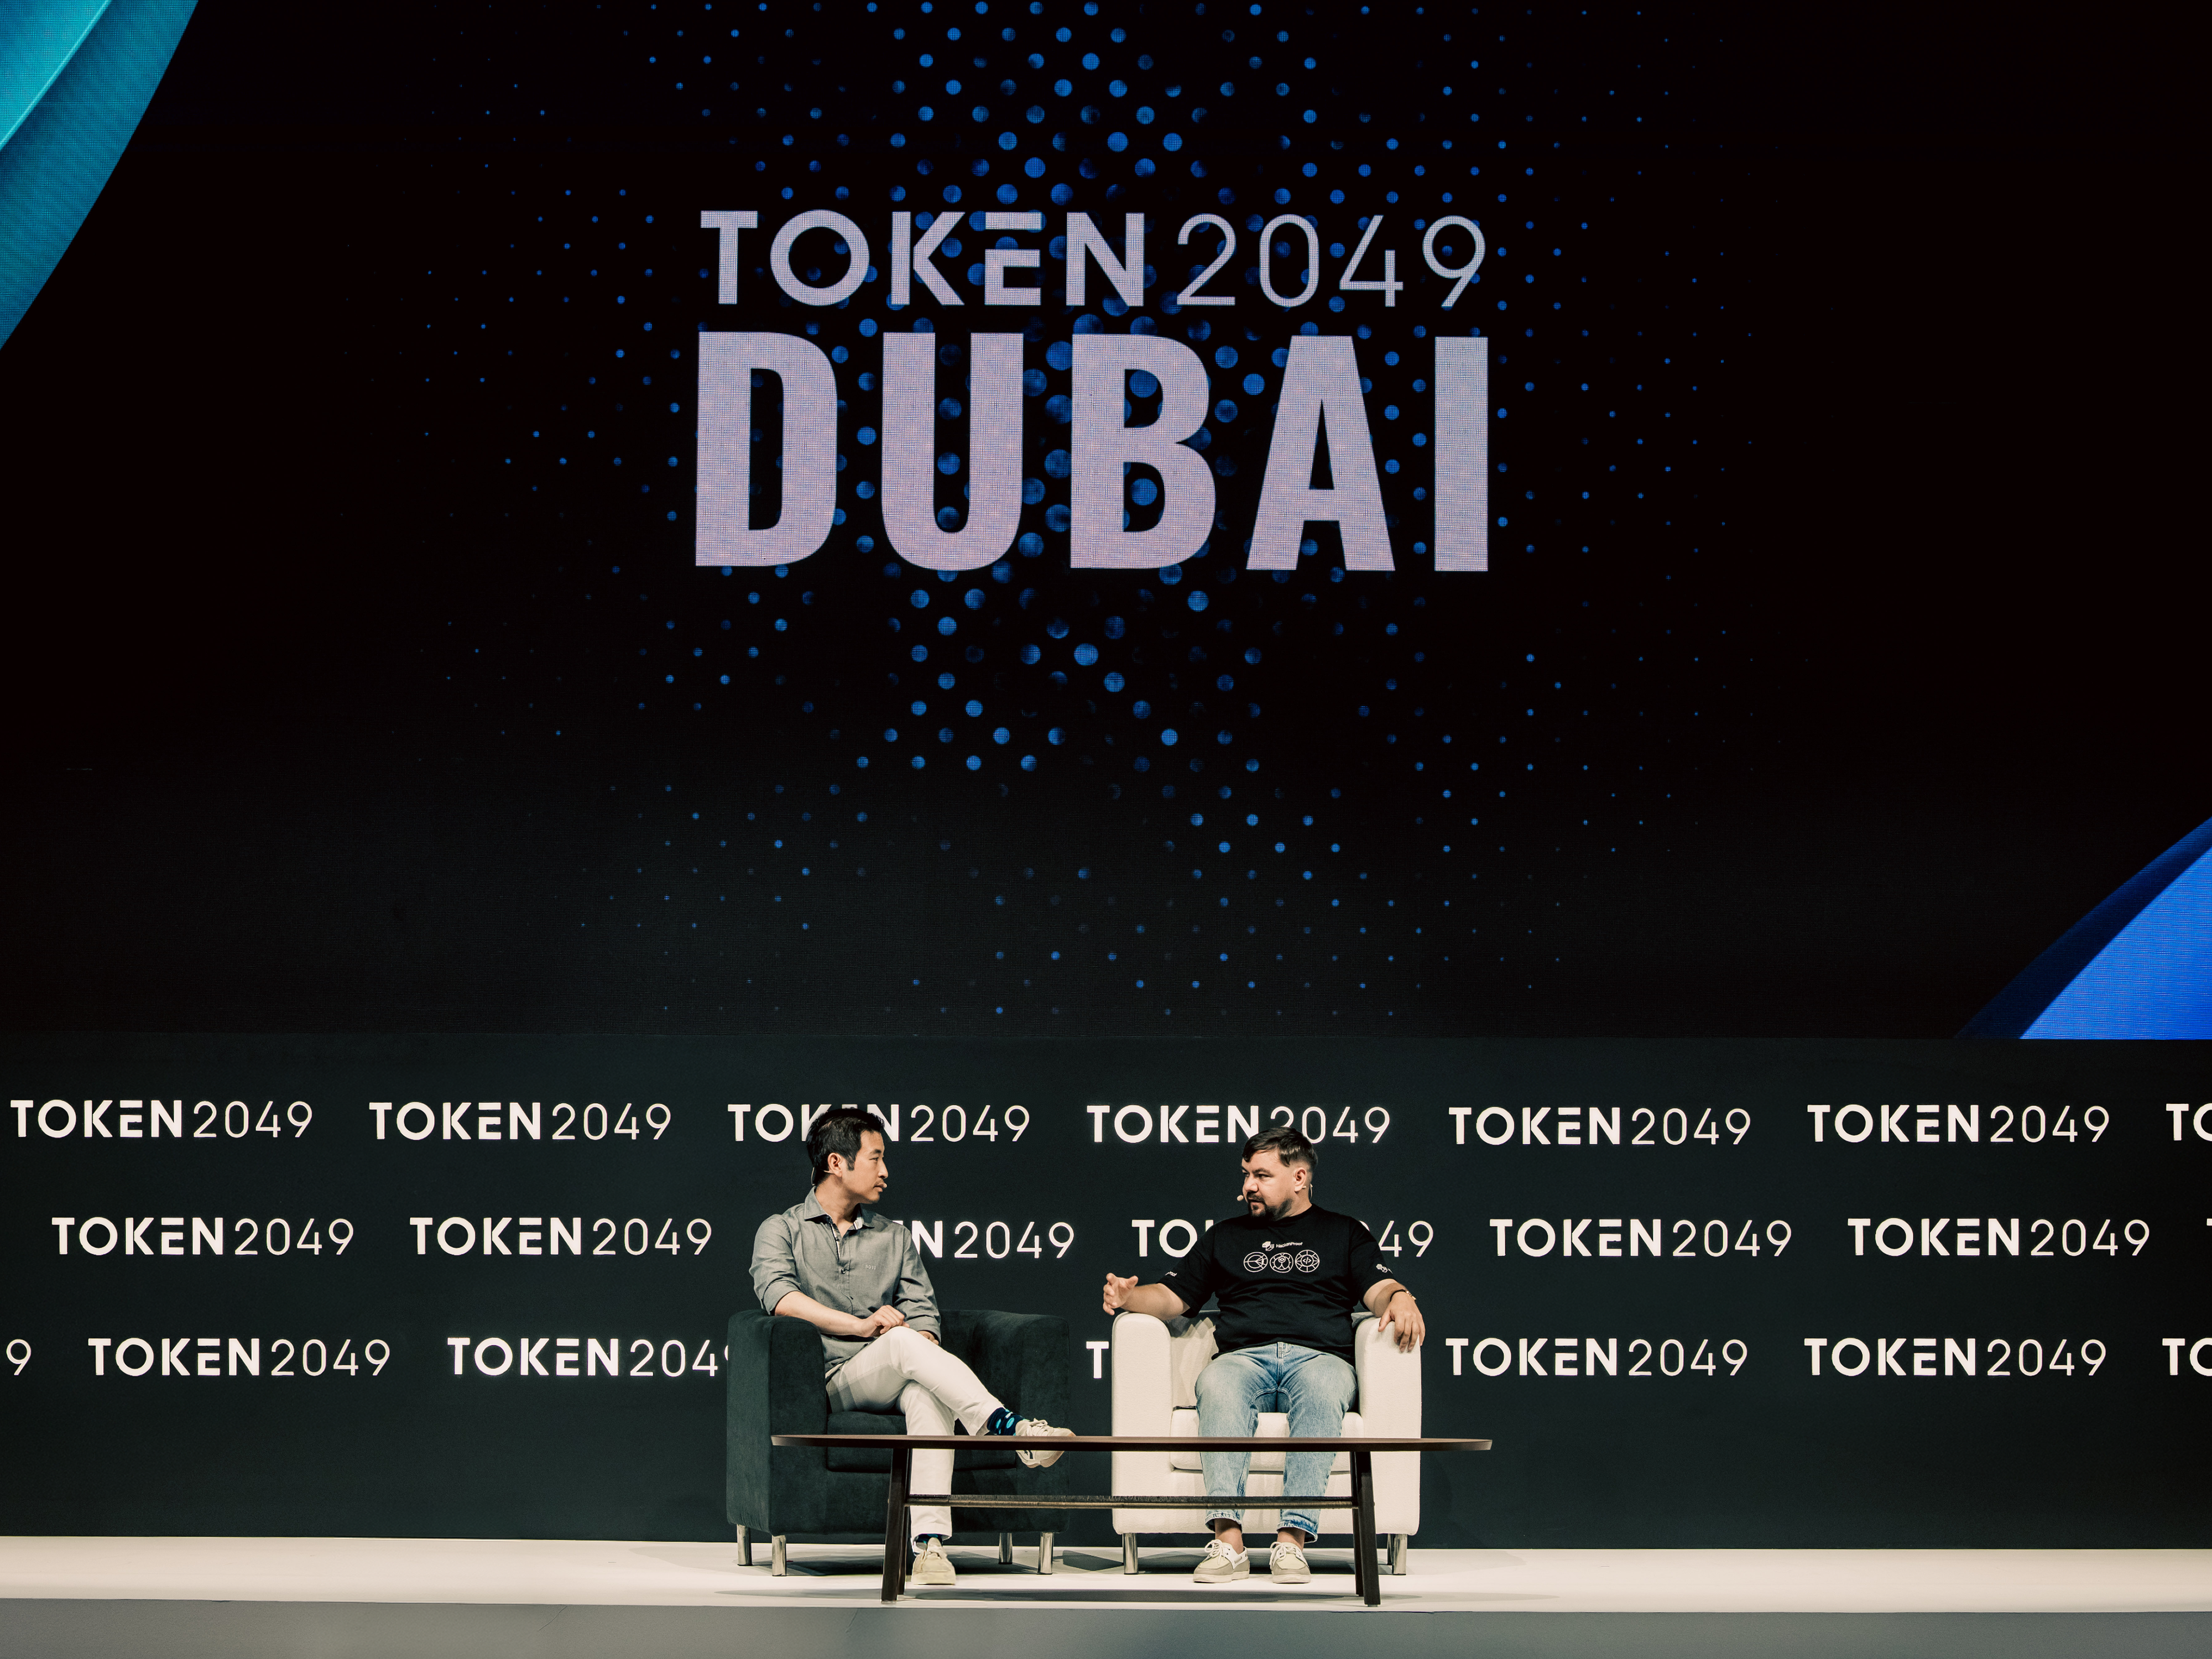
Dmytro Matviiv, CEO, HackenProof
The cost of such inattention is measured in concrete figures. Specifically, according to IBM data, in 2024 the average cost of a data breach for the industrial sector was $5.56 million — the third-highest figure among 17 industries studied. And according to research by ITIC, a technology consulting firm, the average cost of one hour of downtime exceeds $300,000 for more than 90% of medium and large enterprises.
In today’s business environment, where personal accounts, online payments, and customer services operate 24/7, classic penetration testing — assessing a system’s security through a controlled simulation of a cyberattack — once or twice a year is no longer enough. It captures the state of a system only at the moment of the check, but every new code release the next day can open up new potential risks.
The Bug Bounty Platform Philosophy: How HackenProof Manages Risk
Bug bounty is a model in which a company grants controlled access to its code and systems for review by independent researchers. If a white-hat hacker finds a problem, they receive a reward.
According to HackenProof, the average value of a critical vulnerability on the platform ranges from $5,000 to $20,000, and in some large-scale infrastructures reaches hundreds of thousands of dollars.
ʼCompare that to the potential losses from a hacker attack, where the average cost of an incident is measured in the millions. And that’s just the direct financial losses. There are also indirect ones — reputational damage and customer data leaks, which cost businesses even more,ʼ says HackenProof. ʼInvesting in bug bounty delivers a tremendous return on investment: a business pays a relatively small premium for an identified risk instead of incurring losses.ʼ
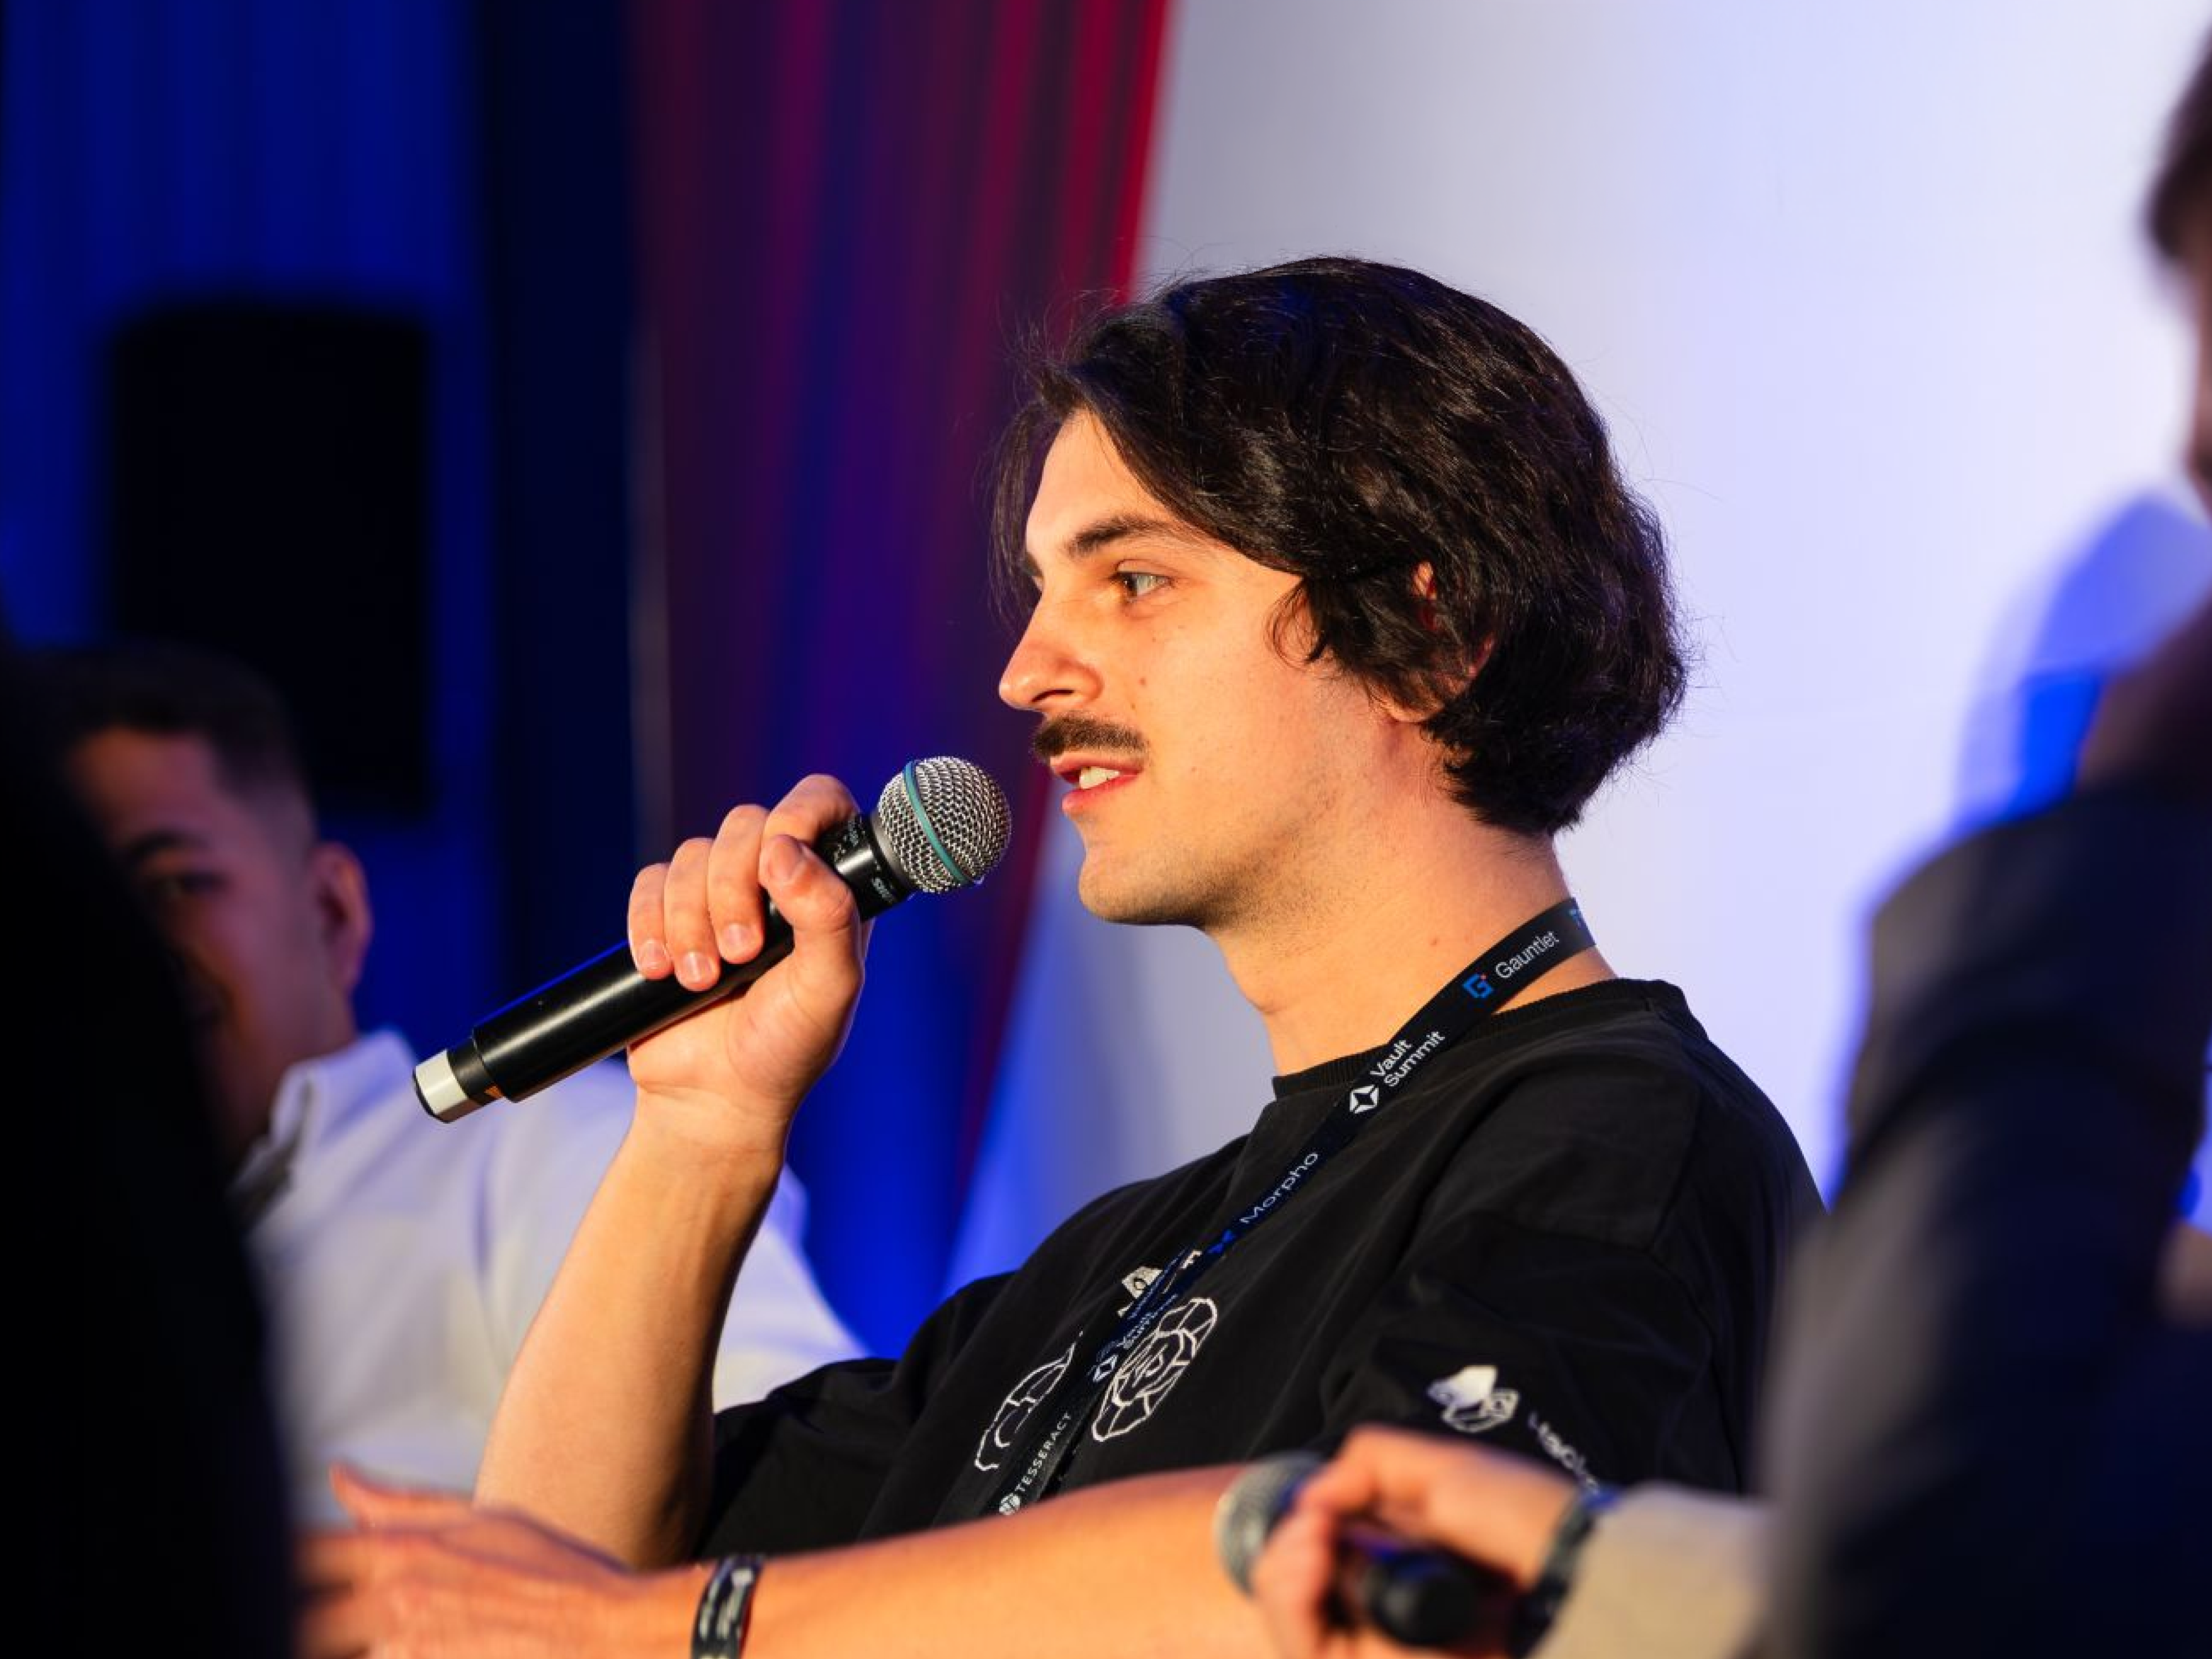
Oleksandr Horlan, CTO, HackenProof
HackenProof is a bridge between business and a community of more than 82,000 ethical hackers. The scale of the platform:
- 400+ bug bounty programs launched;
- $26 million+ paid out to researchers in rewards;
- More than $95 billion in total asset value and market capitalization under the platform’s protection.
The platform helps filter out noise and verify reports of potential vulnerabilities. HackenProof not only assesses the quality of reports but also verifies researchers’ identities (KYC – Know Your Customer), coordinates communication with them, and ensures reward payouts. This allows companies to centralize report management and researcher interaction through a single platform.
According to HackenProof’s internal statistics, among thousands of reports from ethical hackers, 5% to 12% contain critical vulnerabilities — flaws that can potentially affect a product’s business logic, access to customer accounts and data, and, depending on the specific system, create a risk of financial loss.
A Pass to Global Markets: Regulatory Requirements and New European Standards
For Ukrainian businesses integrating into the European economic space, cybersecurity is no longer a matter of internal initiative — it’s becoming a regulatory requirement.
With the European DORA (Digital Operational Resilience Act) and NIS2 (Network and Information Security Directive 2) regulatory frameworks now in force, requirements for cyber risk management are becoming stricter. In particular, DORA sets requirements for ICT risk management, incident reporting, and digital resilience testing for financial institutions within its scope — including banks, payment institutions, and investment and insurance companies.
Launching a bug bounty program through HackenProof allows companies not only to identify and fix weaknesses in their code, but also to strengthen compliance with international security requirements, boosting investment appeal and the trust of Western partners.
Expertise and Work with Leading Brands
Among those who entrust their security to the HackenProof platform are leading players in fintech, banking, e-commerce, transportation, technology, government services, and regulatory bodies, as well as institutional clients.
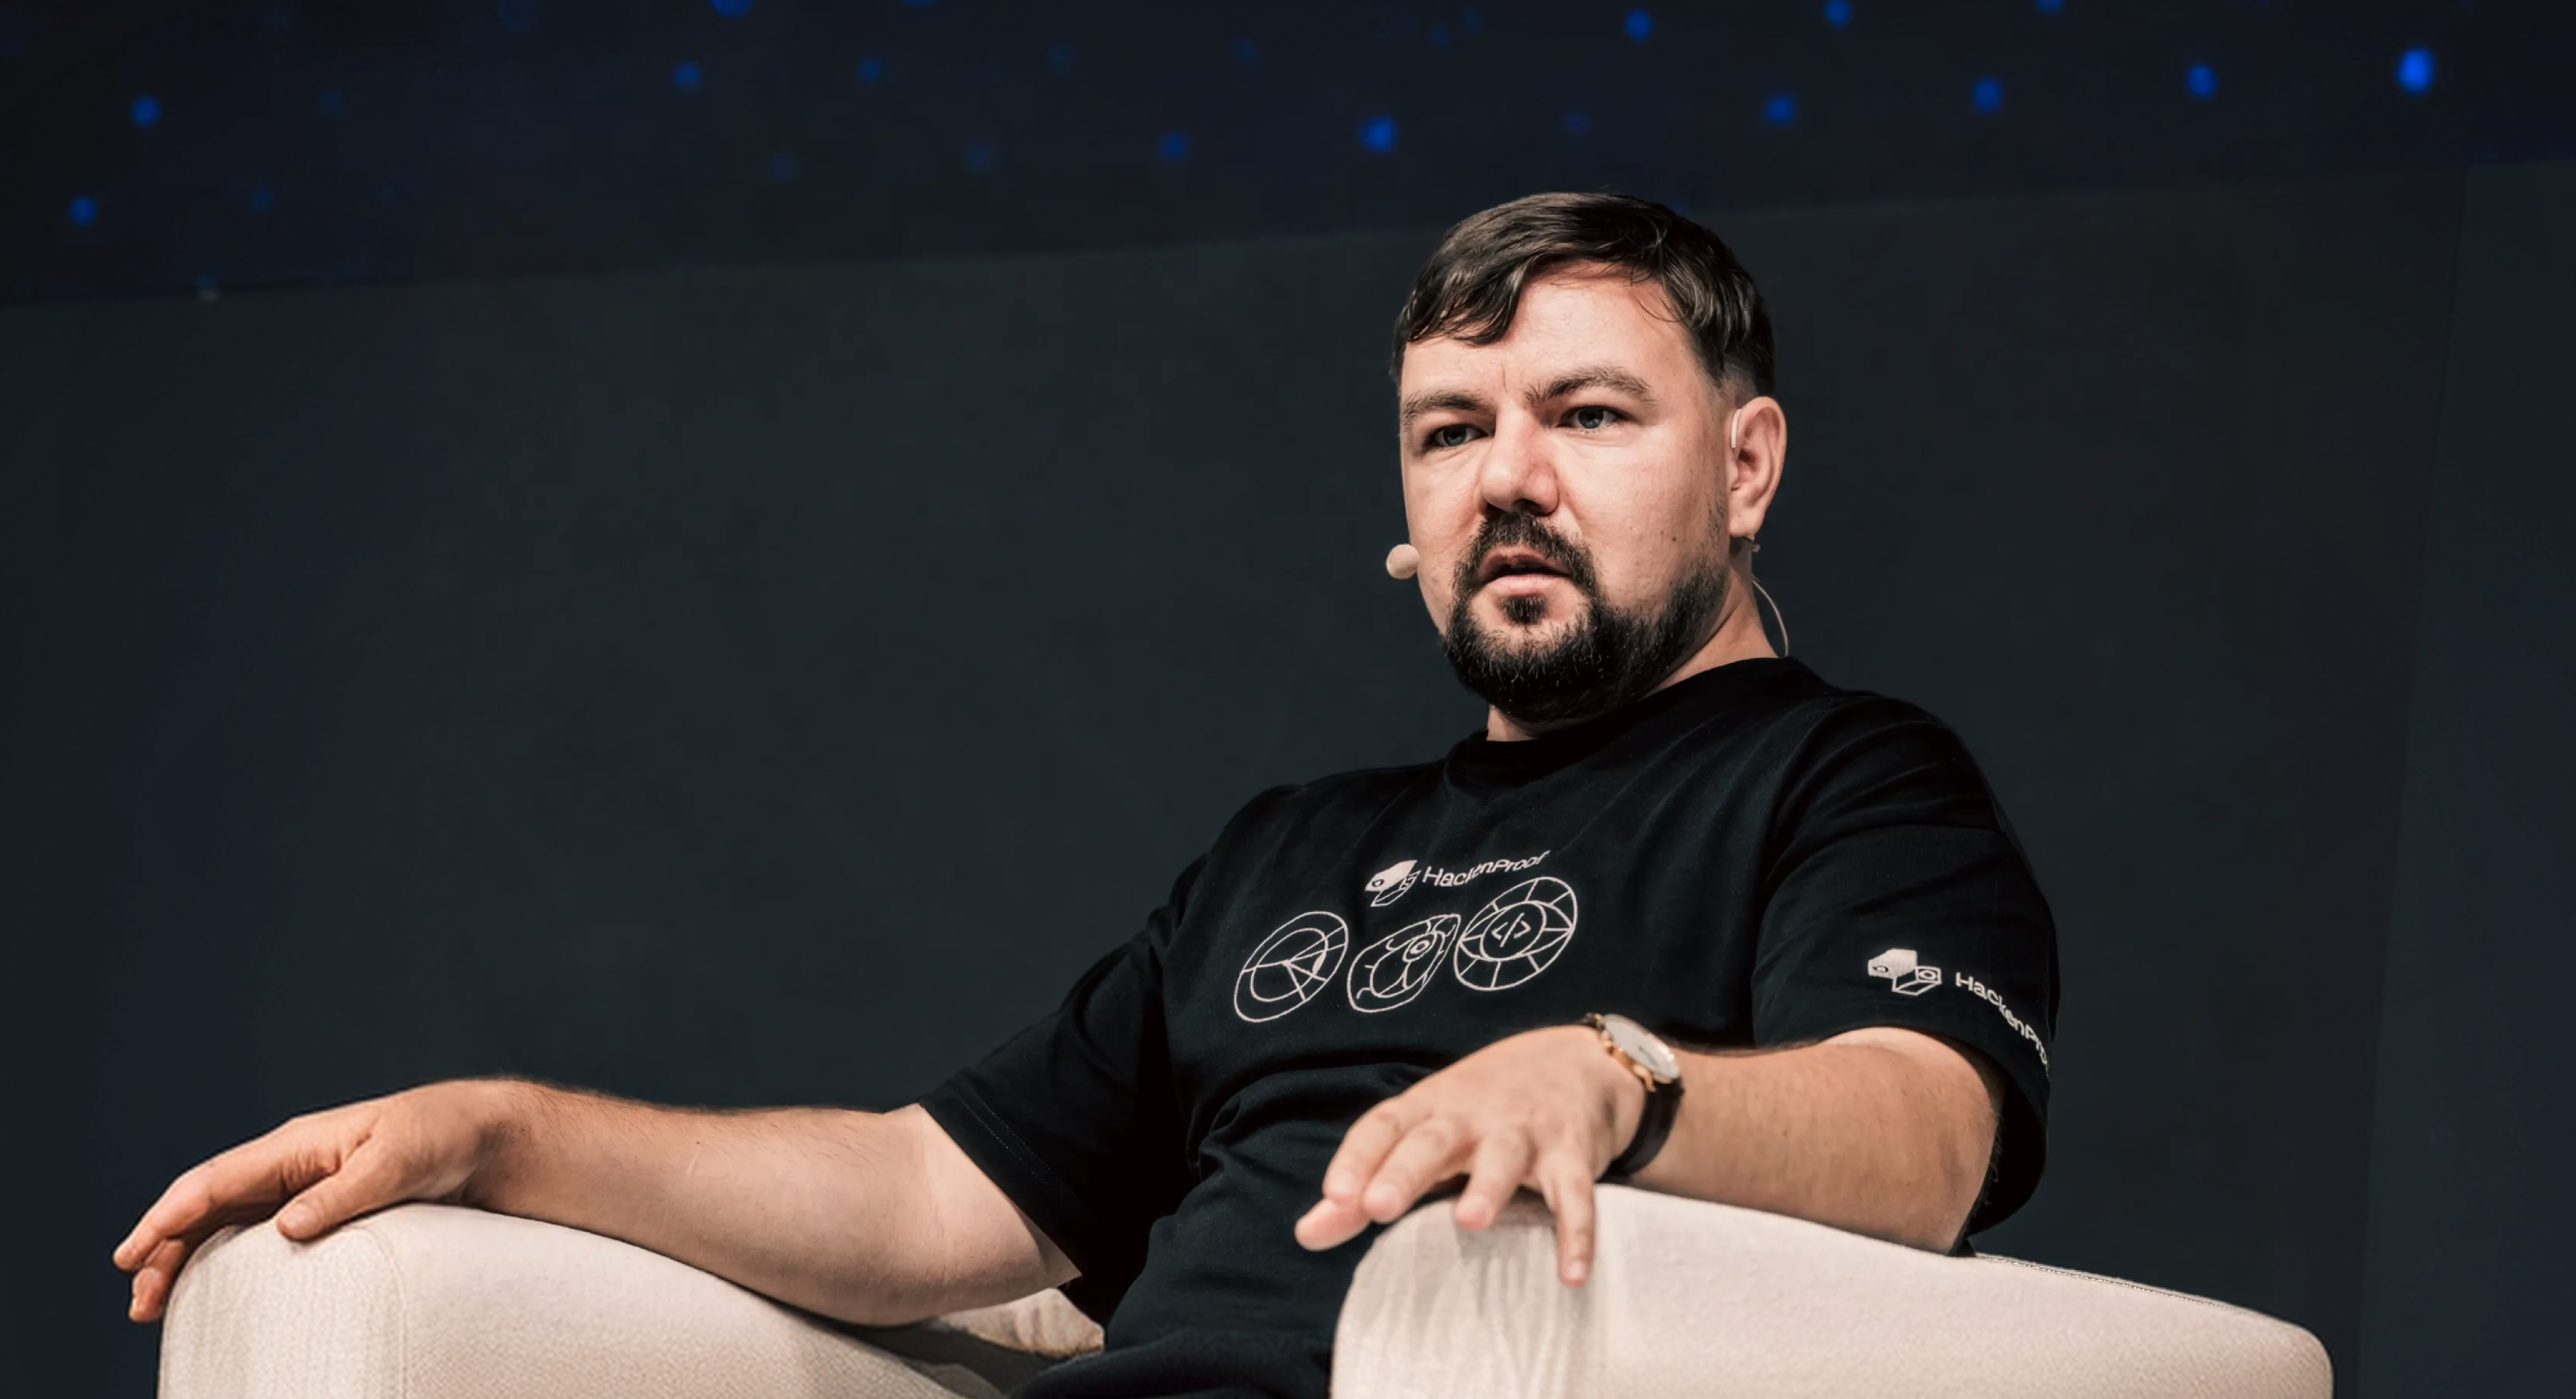
Dmytro Matviiv, CEO, HackenProof
HackenProof’s clients and partners in bug bounty, audits, or joint cyber initiatives include PUMB, Raiffeisen Bank Ukraine, the Defense Intelligence of Ukraine (HUR), Prozorro, Uklon, Tickets Travel Network, and WhiteBit, as well as international technology institutions Ethereum Foundation, Aurora Labs, and NEAR Protocol.
The scale of the task also determines the scale of the reward.
Dmytro Matviiv,
CEO, HackenProof
In 2026 alone, the largest individual payout to an ethical hacker on the HackenProof platform reached $1,000,000 — and it’s not a one-off case. This case perfectly illustrates the economics of bug bounty: it’s far more advantageous for a company to pay a million dollars to a researcher who found a hole in the system and helped close it than to lose hundreds of millions — and its reputation — as the result of a real breach.
How Business Can Strengthen Cyber Defense
Last year alone, CERT-UA (Computer Emergency Response Team of Ukraine), the government team responsible for responding to cyber incidents, handled nearly 6,000 cyber incidents. Against this backdrop, systematic risk monitoring and timely vulnerability detection are becoming increasingly important for business.
Oleksandr Horlan,
CTO, HackenProof
In an era when attackers are using AI to scale up attacks, traditional defense methods don’t always keep pace with change. Companies should use new capabilities to detect and fix vulnerabilities faster. In particular, businesses shouldn’t rely solely on one-off checks: any new code release can create a new potential vulnerability. Security needs to be just as dynamic as development itself.
It’s worth combining penetration testing with bug bounty: the former captures the state of a system on a specific date, while the latter complements this approach with the ongoing search for vulnerabilities by independent researchers. It’s also important to build transparent communication channels: a convenient platform for submitting reports helps ethical hackers promptly notify a company of the issues they’ve found.
The future of cybersecurity lies in collaboration between business, technology platforms, and the global community of ethical hackers. Through HackenProof, companies gain the ability to supplement their own security processes with outside expertise and act proactively.
The first step is a free consultation with a HackenProof expert, which will help assess a product’s current security posture and identify potential areas for strengthening cybersecurity.